Chinese Hackers Breach Nuclear Agency, Global Systems Via Microsoft Flaws
Sophisticated State-Sponsored Groups Exploit SharePoint Vulnerabilities, Compromising U.S. Government and International Organizations
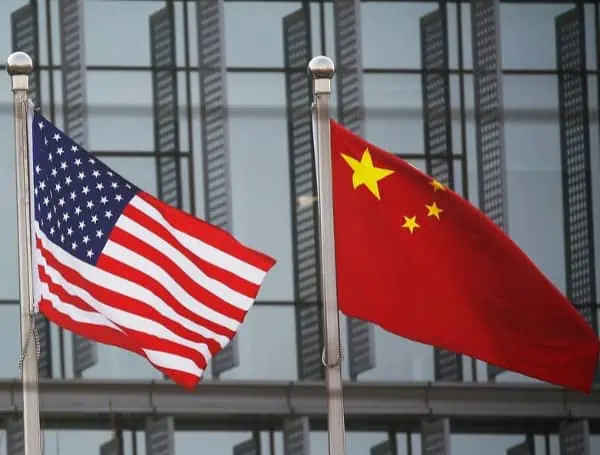
Chinese state-sponsored hacking groups have exploited critical vulnerabilities in Microsoft software to infiltrate sensitive systems worldwide, including those of the U.S. government agency responsible for overseeing the nation’s nuclear weapons, Bloomberg News reported on Tuesday.
Microsoft alerted its customers to the breaches, identifying “Linen Typhoon,” “Violet Typhoon,” and “Storm-2603″—groups believed to be backed by the Chinese government—as the perpetrators. These sophisticated actors targeted flaws within Microsoft’s SharePoint document sharing software, enabling them to gain unauthorized access to internal files and systems across a broad spectrum of organizations.
Despite Microsoft having released patches for the security gaps, cybersecurity researchers have already confirmed that over 100 servers tied to approximately 60 organizations have been successfully infiltrated. Among the most concerning breaches is that of the U.S. National Nuclear Security Administration (NNSA), a semi-autonomous agency under the Department of Energy (DOE) tasked with managing the nation’s nuclear arsenal, supplying nuclear reactors for the U.S. naval fleet, and responding to nuclear terrorism and proliferation.
A source familiar with the breach informed Bloomberg News that while multiple systems at the DOE were compromised, there is currently no indication that classified or sensitive data has been stolen. The DOE has not yet responded to requests for comment.
Beyond the NNSA, other U.S. government entities impacted include the Department of Education, Florida’s Department of Revenue, and the Rhode Island General Assembly. Experts warn that as many as 10,000 organizations globally could be at risk from these exploited vulnerabilities. Silas Cutler, a researcher at the Michigan-based cybersecurity firm Censys, described the situation to Bloomberg News as “a dream for ransomware operators,” predicting continued malicious activity.
Chinese officials have vehemently denied allegations of government involvement, dismissing them as “smears.” However, a February 2024 report from the Office of the Director of National Intelligence identified China as America’s primary cybersecurity adversary, posing a significant threat to both government and private sector entities. This latest incident follows closely on the heels of other high-profile breaches, including the 2023 compromise of email accounts belonging to the U.S. Commerce and State Departments, affecting even the U.S. ambassador to China.
Concerns about China’s cyber capabilities extend beyond data theft. Former National Security Adviser Jake Sullivan reportedly informed then-President Joe Biden in 2023 that Chinese cybercriminals possess the capacity to disrupt large segments of the U.S. power grid and major American ports, according to The Wall Street Journal.
Adding another layer of complexity to the situation, a recent ProPublica investigation revealed that for over a decade, Microsoft had been utilizing “digital escorts”—low-paid workers with security clearances but often limited technical expertise—to input commands from more skilled China-based engineers into U.S. Department of Defense networks. Microsoft announced on July 18 that it would cease this practice following concerns from national security and cybersecurity experts regarding potential access to sensitive government data by these engineers.
MORE ARTICLES - TAMPA FREE PRESS
- Pentagon Stikes Blow To ‘America Last’ Orgs With New Order
- Biden-Appointed Judge Ditches Lawsuit Against Sanctuary City Chicago
- Deep Blue California Curbs Legal Aid For Felon Immigrants, Sparks Outcry
- Border Czar Tom Homan: No “Free Pass” For Illegal Entry
- Still Fighting: Vets Seek Justice After Being Ousted Over Vaccine Mandate
- Ohio Rep. Jim Jordan’s Weaponization Report Ignites New Battle Over Government Power
- SIJ Program Rocked By Gangs, Criminals, And Terror Suspects: National Security Alarms Sounded
- Former Democrat Party Strategist Dan Turrentine Says Dems Are Quietly Backing This Trump Policy
- White House Cracks Down On ‘Woke AI’ In Federal Procurement
TAMPA FREE PRESS
Please make a small donation to the Tampa Free Press to help sustain independent journalism. Your contribution enables us to continue delivering high-quality, local, and national news coverage.
Android Users: Download our free app to stay up-to-date on the latest news.
Connect with us: Follow the Tampa Free Press on Facebook and Twitter for breaking news and updates.
Sign up: Subscribe to our free newsletter for a curated selection of top stories delivered straight to your inbox.