Microsoft Hit By Dual Crises: Global Server Outages And Active Outlook Security Hack
Microsoft faced a turbulent Thursday on two separate fronts, battling widespread server outages across its email and workplace apps while federal officials warned that hackers are actively exploiting a hidden flaw in Microsoft Outlook to steal login data.
The technical disruptions began earlier in the day with a brief snag in Microsoft Teams that left users in North America unable to access certain features. While Microsoft quickly resolved that issue—stating its “mitigative actions have successfully restored service health and functionality”—a much larger headache soon followed for Exchange Online mailbox users.
Initially reported across the Americas, the email connectivity trouble quickly proved to be a global issue. Outage tracker Downdetector logged widespread user reports across both Teams and Outlook as Microsoft confirmed the disruption “may affect Microsoft 365 service connectivity for users in any region.”
Rather than a sudden surge in user traffic, Microsoft traced the bottleneck to internal hardware dropping offline. “We determined the elevated load isn’t driven by an increase in traffic, but by a number of servers being unexpectedly unavailable; straining the remaining infrastructure,” the company explained in a social media update. Engineers found no recent system changes tied to the crash, instead pointing to an internal monitoring glitch. “Our investigation indicates the failed health checks may originate from a specific component that’s responsible for processing server health,” Microsoft stated.
To contain the fallout, the company halted system rollouts and began shifting data loads. “We’re aggressively pursuing all pathways to reduce impact,” Microsoft said. “We’ve paused all deployments, we’re moving additional traffic off the affected infrastructure, and we’re restarting affected servers to return them to service.”
As engineers worked to restore service, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) confirmed a separate, urgent threat involving Outlook. Federal officials verified that hackers are actively exploiting a previously unknown security flaw—tracked as CVE-2026-124194—in live attacks rather than theoretical tests.
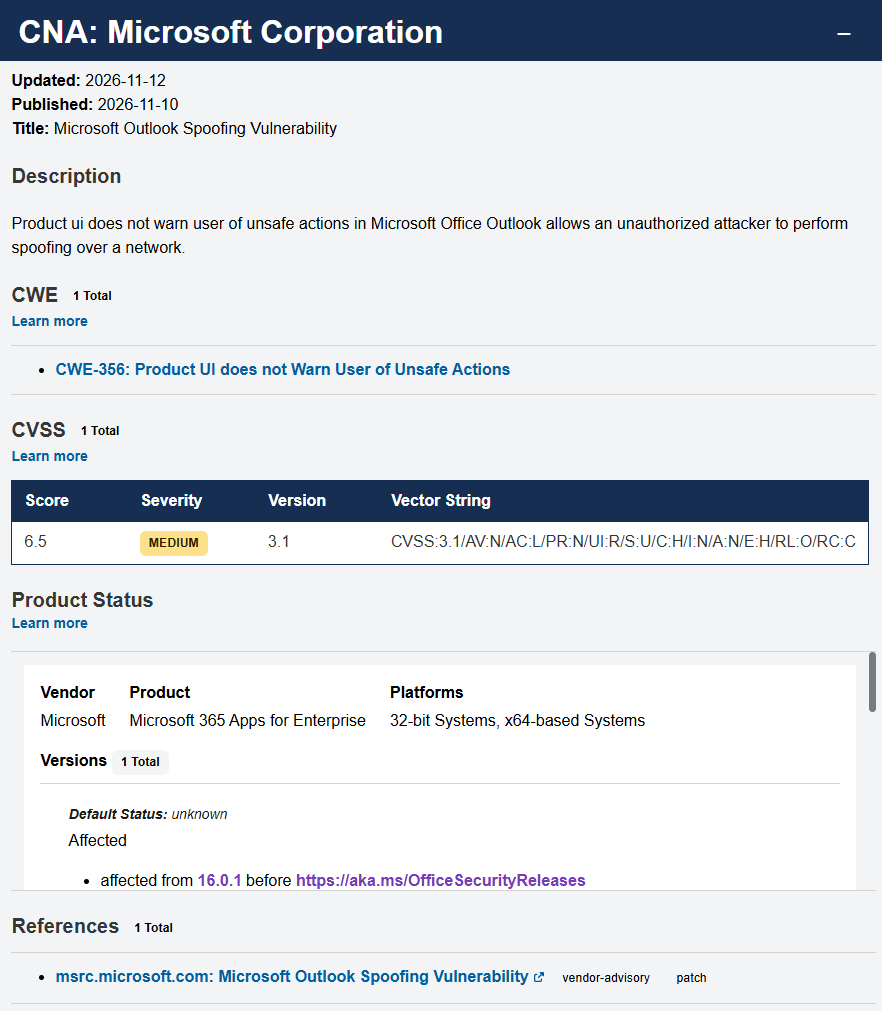
According to a Microsoft security advisory, the exploit relies on tricking a user into opening a specially crafted message file inside Outlook. Once opened, the program silently connects to an external network location controlled by the attacker, completely bypassing the warning prompt Outlook normally displays for outside content. That silent connection lets hackers capture sensitive authentication data without needing prior login access to the target’s system.
Microsoft classified the bug as a network-spoofing vulnerability with a severity score of 6.5 out of 10. Because attackers weaponized the flaw before a fix was widely available, it qualifies as a zero-day vulnerability. Microsoft has released security patches to close the loophole, and federal authorities are urging users and IT teams to install the updates immediately while remaining cautious of unexpected message files.
Neither Microsoft nor CISA has disclosed how many people or organizations have been compromised by the security flaw so far, nor whether there is any connection between the hack and Thursday’s server outages.